RSA Authenticator (SecurID)
- Rating
- 3.2
- Downloads
- 10,000,000+
- Age
- Everyone
Additional Info
- App Name
- RSA Authenticator (SecurID)
- Category
- Communication
- Package Name
- com.rsa.securidapp
- Developer
- RSA Security
- Rating
- 3.2
- Version
- 4.6.0.16
 Analysis by Appcrazy
When an app sits between me and a work account, convenience matters, but trust matters more. RSA Authenticator, also known as SecurID, is a communication app from RSA Security built around that exact moment: proving that I am really the person trying to sign in. I used it less like a normal messaging tool and more like a compact security checkpoint that stays ready when an organization asks for an extra verification step.
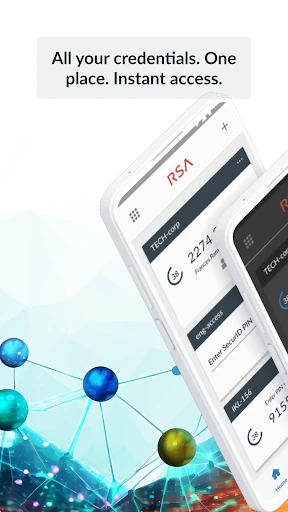
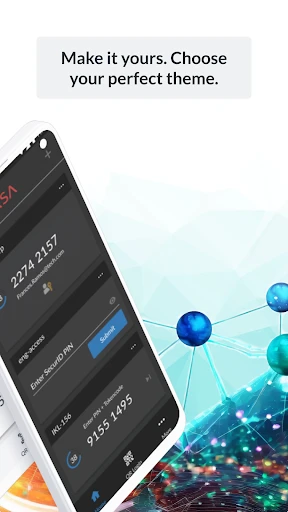
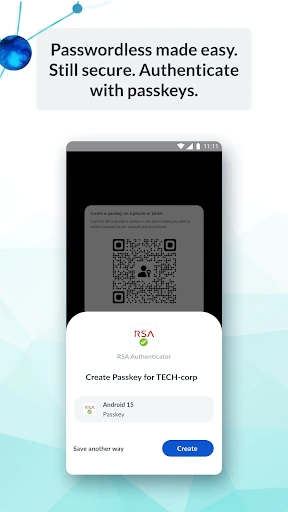
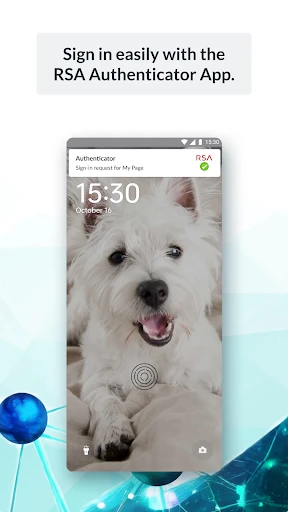
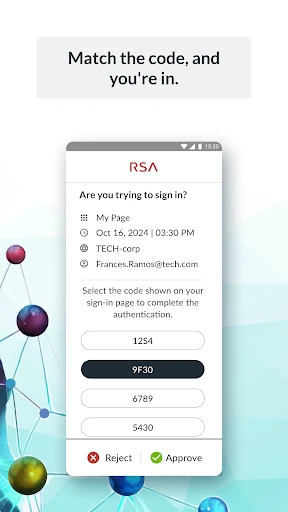
The central capability is authentication through several methods, including passkeys, biometrics, and one-time passwords. That combination gives the app a broader role than a simple code generator. In my experience, the most useful part is not having every method available at once; it is being able to use the method that fits the account and the security setup behind it. Some sign-ins can feel almost immediate with a passkey or fingerprint, while others still depend on entering a temporary code.
My main takeaway is simple: RSA Authenticator is strongest when it is part of an organization’s existing SecurID setup, not when someone downloads it hoping it will independently secure every personal account. That distinction affects the entire experience, from the first setup to what happens when changing phones or trying to sign in without a convenient biometric option.
What the authentication capability changes in everyday use
A password is something I type and reuse mentally. An authenticator adds a separate proof that is generated or stored on a device I control. That extra step can make a login slightly slower, but it also means a stolen password alone is less useful to someone else. RSA Authenticator focuses on that second layer rather than trying to replace the services I access.
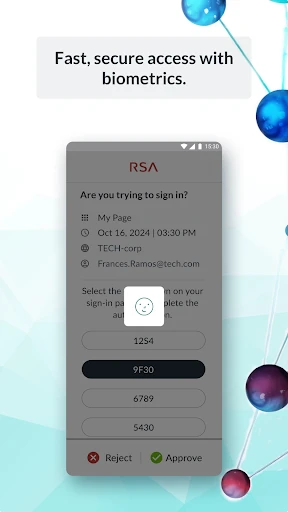
The app’s support for passkeys and biometrics is important because it can reduce the familiar friction of reading a code and typing it into another screen. When the sign-in flow supports those methods, I can verify myself using a device-based credential or a fingerprint rather than manually copying digits. That is a meaningful improvement during a busy workday, especially when I am switching between a laptop and a phone.
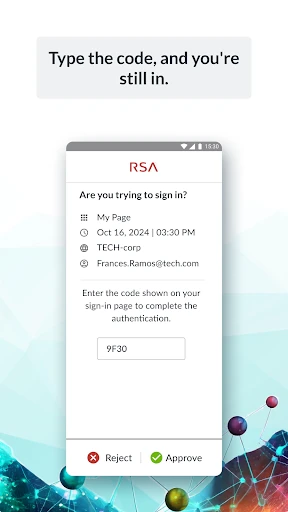
One-time passwords remain valuable because they work as a familiar fallback in environments that have not moved fully to passkeys. A temporary code is less elegant than a biometric prompt, but it is understandable and widely used in business access systems. The result is a practical mix: modern authentication where the account supports it, and a code-based route where older or more rigid systems still require one.
It is worth separating the app from the service being protected. RSA Authenticator does not magically add a security layer to an arbitrary website just because it is installed. The account administrator or service has to support the relevant RSA authentication process, and setup normally depends on the enrollment information supplied by that organization. For a personal user browsing the app store without an employer or service instruction, that can make the first launch feel less self-explanatory than a consumer-focused authenticator.
Catch Up on the Latest Stories
Microsoft Teams on Mobile Keeps Work Moving, If You Keep It Tidy
Groupon Turns Local Discounts Into a Marketplace, With a Catch
App of the Week: Yandex Go Makes City Errands Easier
Make Xiaomi Weather Work Harder with Smarter Settings and Daily Routines
Boomplay Turns Music Streaming Into a Daily Discovery Habit
Google Docs on Mobile Keeps the Page in Focus, Until Formatting Gets in the Way
The app is free, carries an Everyone age rating, and has been available since May 24, 2011. Its long presence is consistent with its enterprise-oriented identity: this is a tool intended to remain part of an access routine, not an app designed around entertainment or social discovery. It has passed the ten-million-install mark and holds an average rating of 3.2 from around eighteen thousand ratings, with roughly twelve hundred written reviews. Those figures suggest a widely used but not universally smooth experience, which matches the way authentication apps often depend on external setup.
Passkeys, biometrics, and codes are not interchangeable
In practical terms, each method solves a different problem. A passkey can make sign-in feel cleaner because I am not handling a temporary number. Biometrics can make the confirmation quick when my device recognizes me. An OTP is more manual, but it remains useful when a service asks for a code or when the preferred method is unavailable.
That flexibility also creates a responsibility: I need to know which method the account expects before assuming the app will provide a one-tap login. If I am helping a colleague, I would first check the organization’s enrollment instructions rather than repeatedly trying random options. Authentication failures are often caused by an incomplete registration or a mismatch between the account’s policy and the method selected, not by the visible code screen itself.
A less obvious advantage is workflow continuity. If my normal sign-in uses biometrics but a particular access request presents an OTP challenge, having both concepts in the same authentication app means I do not need to maintain a separate mental system for every service. That does not remove the need for careful account recovery, but it can reduce the number of security tools I have to open during a normal work session.
How I would use it in practice
The first step is not simply installing the application. I would install it when an employer, school, or supported service tells me to enroll an account. The enrollment stage is the foundation: without the correct registration details, the app may be present on the phone but unable to prove anything useful. This is one of the biggest differences between RSA Authenticator and a casual utility that begins working immediately after scanning a code.
Once the account is enrolled, the daily pattern is straightforward. I start a sign-in on the service I need, respond to the authentication request using the available method, and return to the original sign-in if a code is required. With a biometric or passkey flow, the interaction can be brief. With an OTP, I need to read the current value and enter it before it becomes invalid.
For a realistic example, imagine that I am working from home and open a company dashboard on my laptop. My password is accepted, but the organization requires a second check. I open RSA Authenticator on my phone, use the available biometric confirmation if that account supports it, and complete the sign-in. If the dashboard instead requests a one-time password, I copy the displayed value carefully and submit it before switching back to the laptop. The app’s value in this situation is not that it makes the laptop smarter; it gives the laptop a separate, phone-based proof.
That cross-device workflow is where I noticed the most practical friction. The phone is doing the verification while the computer is doing the work, so I need both devices nearby and unlocked enough to complete the process. If the phone battery is empty, unavailable, or replaced, the authentication routine can stop even though the laptop and password are working. I would not treat the app as a reason to abandon every other recovery method offered by the organization.
Biometric protection is convenient, but I would still pay attention to the fallback behavior on my device. A fingerprint or similar confirmation may be the fastest route during routine access, while a device passcode can become necessary under certain phone conditions. The important point is to understand the phone’s own unlock rules and not assume that a biometric prompt will always appear.
For OTP use, I recommend checking the digits slowly rather than relying on memory. The code is temporary, and entering an old value after waiting on another screen can lead to a confusing failure. If a code does not work, I would avoid repeatedly guessing. I would check that the account selected is the right one, confirm that the current code is being used, and then follow the organization’s support process if the problem continues.
A better setup routine before the first important login
I would complete enrollment before the moment I urgently need access. After setup, I would perform a normal test sign-in while I still have access to the administrator or help desk. This catches practical issues such as an account that was not enrolled correctly, a phone that is not the intended device, or a login flow that expects an OTP instead of a biometric confirmation.
I would also make the app easy to reach without making the phone itself careless. Keeping it visible enough for quick access is useful, but the phone should still have a proper screen lock. The authenticator is part of the security chain; convenience should not mean leaving the device openly accessible to anyone who picks it up.
A particularly useful habit is to distinguish “the app is broken” from “the account is not configured for this method.” If a passkey option does not appear, that may reflect the service’s policy rather than a missing button. If an OTP is rejected, the cause may be enrollment or timing. Thinking in those categories prevents unnecessary reinstalling, which can create more trouble if the account needs to be registered again.
The scenario where RSA Authenticator makes the most sense
I see the clearest fit for employees and contractors who access protected company systems from a computer while using a phone as a separate authentication device. In that setting, the app is not competing with a password manager or a social app; it is fulfilling a specific access requirement. The combination of passkeys, biometrics, and OTPs gives the organization room to support different authentication policies without asking every user to learn a completely different tool.
It can also suit people who regularly move between office and remote work. A phone-based authenticator travels with me, while the protected services may be hosted on several computers or accessed through different networks. The authentication device remains separate from the machine I am using, which is a sensible arrangement for accounts containing business information.
Another good scenario is a mixed environment in which some systems have adopted newer sign-in methods and others still ask for a code. I would rather have one clearly defined authentication app for that transition than keep one tool for passkeys, another for biometric approval, and a third for OTPs. The benefit is organizational rather than flashy: fewer places to look when a login challenge appears.
That said, I would not recommend installing it casually for someone who only wants to protect a handful of personal accounts and has no instruction to use RSA Security’s system. A consumer authenticator that is designed around direct QR-code enrollment may be easier for that person. RSA Authenticator’s strengths become visible when the account and the app are part of the same managed authentication arrangement.
Where the trade-offs become noticeable
The biggest limitation is dependency on the surrounding account setup. The app can present authentication methods, but it cannot decide whether a website, employer portal, or internal system accepts them. This makes the experience feel excellent in a properly configured environment and unnecessarily confusing in an unsupported one. I would check compatibility with the service administrator before choosing it as my main authenticator.
There is also a phone-dependency trade-off. A separate mobile device is useful because it keeps the second factor away from the computer, but it adds another object that must be charged, protected, and available. Travel, phone replacement, or a lost device can turn a simple login into an account-recovery task. Before relying on the app for critical work, I would learn the organization’s approved replacement and recovery procedure.
OTP authentication is dependable as a concept, but it is not frictionless. Reading a temporary number, switching applications, and typing it correctly takes more effort than a biometric confirmation. It can also be awkward when I am already using the phone for another task. I consider OTP support a valuable compatibility layer rather than the most pleasant part of the experience.
Passkeys and biometrics improve speed, but their convenience depends on device support and account enrollment. They are not a universal shortcut that overrides the organization’s policy. If a service has not enabled a particular method, I cannot force the app to offer it. This is a subtle but important expectation to set before judging the application after one unsuccessful attempt.
The rating of 3.2 reflects why expectations should stay practical rather than idealistic. Authentication apps are judged during stressful moments, often when a user is locked out or facing a setup error. A polished interface cannot solve every enrollment problem, and a user may reasonably blame the app when the real issue sits between the account administrator, the device, and the sign-in service. I would evaluate it as part of that complete system.
The current version is 4.6.0.16, and the minimum operating-system requirement is version 9. That makes the app accessible to many still-supported devices, but I would check the phone’s software before planning a deployment across a team. For an individual user, the more important question is whether the phone can run the app reliably and whether the organization supports the exact authentication path being requested.
How it compares with familiar alternatives
Compared with a basic OTP-only authenticator, RSA Authenticator has a broader authentication role because it also covers passkeys and biometrics. That can reduce manual code entry when the protected service supports a newer method. The trade-off is that a simple OTP app may feel easier to understand for a personal account that only needs a standard rotating code.
Compared with a password manager, this app has a narrower purpose. A password manager is generally built to store and fill credentials, while RSA Authenticator is focused on proving identity during a protected sign-in. I would not choose one as a replacement for the other without checking what the account requires. In a work setup, they can complement each other: one handles the password, and the authenticator handles the additional verification.
Compared with a built-in platform passkey tool, RSA Authenticator can be more useful when an organization specifically directs users into its SecurID workflow or needs OTP compatibility as well. A built-in tool may be more seamless for a personal account that lives entirely inside one device ecosystem. The better choice depends less on brand preference and more on the authentication policy attached to the account.
Who will gain the most from using it
I would recommend RSA Authenticator to people who have received clear enrollment instructions from an organization using RSA Security authentication. Employees signing into internal systems, contractors accessing managed resources, and teams moving between OTP and passkey-based access are the most likely to appreciate it. For them, the app’s value comes from fitting several verification styles into one work routine.
I would be more cautious with a user who wants a universal personal authenticator without any existing RSA connection. The app may not provide the immediate, self-guided setup that person expects, and its usefulness depends heavily on whether the target services support the relevant RSA process. A simpler consumer-focused option may be a better starting point in that case.
I also would not make it the only thing I think about when planning account recovery. The app can make ordinary authentication quick, but access continuity still matters when a phone is lost, changed, damaged, or unavailable. I would keep the organization’s recovery instructions accessible and complete any approved backup enrollment before an emergency occurs.
After using it, my opinion is favorable but specific. RSA Authenticator is not trying to be an all-purpose communication platform despite its store category; it is a focused security companion for authentication. Its support for passkeys, biometrics, and OTPs gives it useful range, while its dependence on proper account enrollment creates the main barrier. If your workplace or supported service already uses RSA Security, I think it is worth installing and learning before you need it. If you are simply looking for a general-purpose personal code generator, I would first compare easier self-service alternatives.
In short, RSA Authenticator earns its place when it turns a required second step into a predictable part of the day. The best result comes from choosing the right method for each account, testing enrollment early, keeping the phone available, and understanding the recovery process. Used that way, it does not eliminate every login interruption, but it can make protected access more secure without making every sign-in feel like a major task.
Pros
- Enhanced security with two-factor authentication.
- User-friendly interface and easy setup process.
- Supports multiple account tokens for convenience.
- Reliable performance with minimal downtime.
- Regular updates and security patches.
Cons
- Requires internet connection for token generation.
- Limited offline functionality for some features.
- Can be complex for non-tech-savvy users.
- Dependent on RSA server availability.
- Might require additional training for full utilization.
Frequently Asked Questions
What is RSA Authenticator (SecurID)?
RSA Authenticator (SecurID) is a mobile application designed to provide an additional layer of security through two-factor authentication (2FA). It is widely used in corporate environments to ensure secure access to sensitive information. The app generates a unique time-sensitive passcode that complements your regular password, enhancing the security of user accounts.
How does RSA Authenticator (SecurID) improve security?
RSA Authenticator (SecurID) enhances security by requiring users to provide two forms of identification before accessing their accounts. Beyond the traditional password, it generates a dynamic, one-time passcode that changes every 60 seconds. This means that even if someone knows your password, they won't be able to access your account without the valid passcode.
Is RSA Authenticator (SecurID) easy to set up and use?
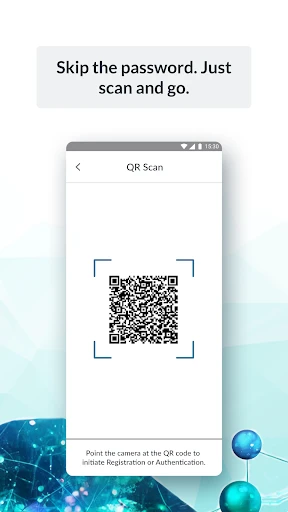
Yes, RSA Authenticator (SecurID) is designed with user-friendliness in mind. Setting up the app is straightforward, involving scanning a QR code or entering a code provided by your organization. Once set up, using the app is simple: just open it to get your current passcode whenever you need to authenticate.
Can I use RSA Authenticator (SecurID) for multiple accounts?
Yes, RSA Authenticator (SecurID) supports multiple accounts, making it convenient for users who need to secure more than one account. Each account can be added separately, and the app will generate unique passcodes for each, ensuring that you maintain strong security across all your accounts.
What should I do if I lose my device with RSA Authenticator (SecurID) installed?
If you lose your device with RSA Authenticator (SecurID) installed, it's crucial to contact your organization's IT support immediately. They can disable the app on the lost device and help you set up a new one. It's important to act quickly to prevent potential unauthorized access to your accounts.